
Permissions have a scope.
An OAuth connection can read information or act on an account. Review its permissions to make a decision in context.
View permissions

Bring together what you know about your tools, their accounts and their access. Then choose a response whose outcome you can track.
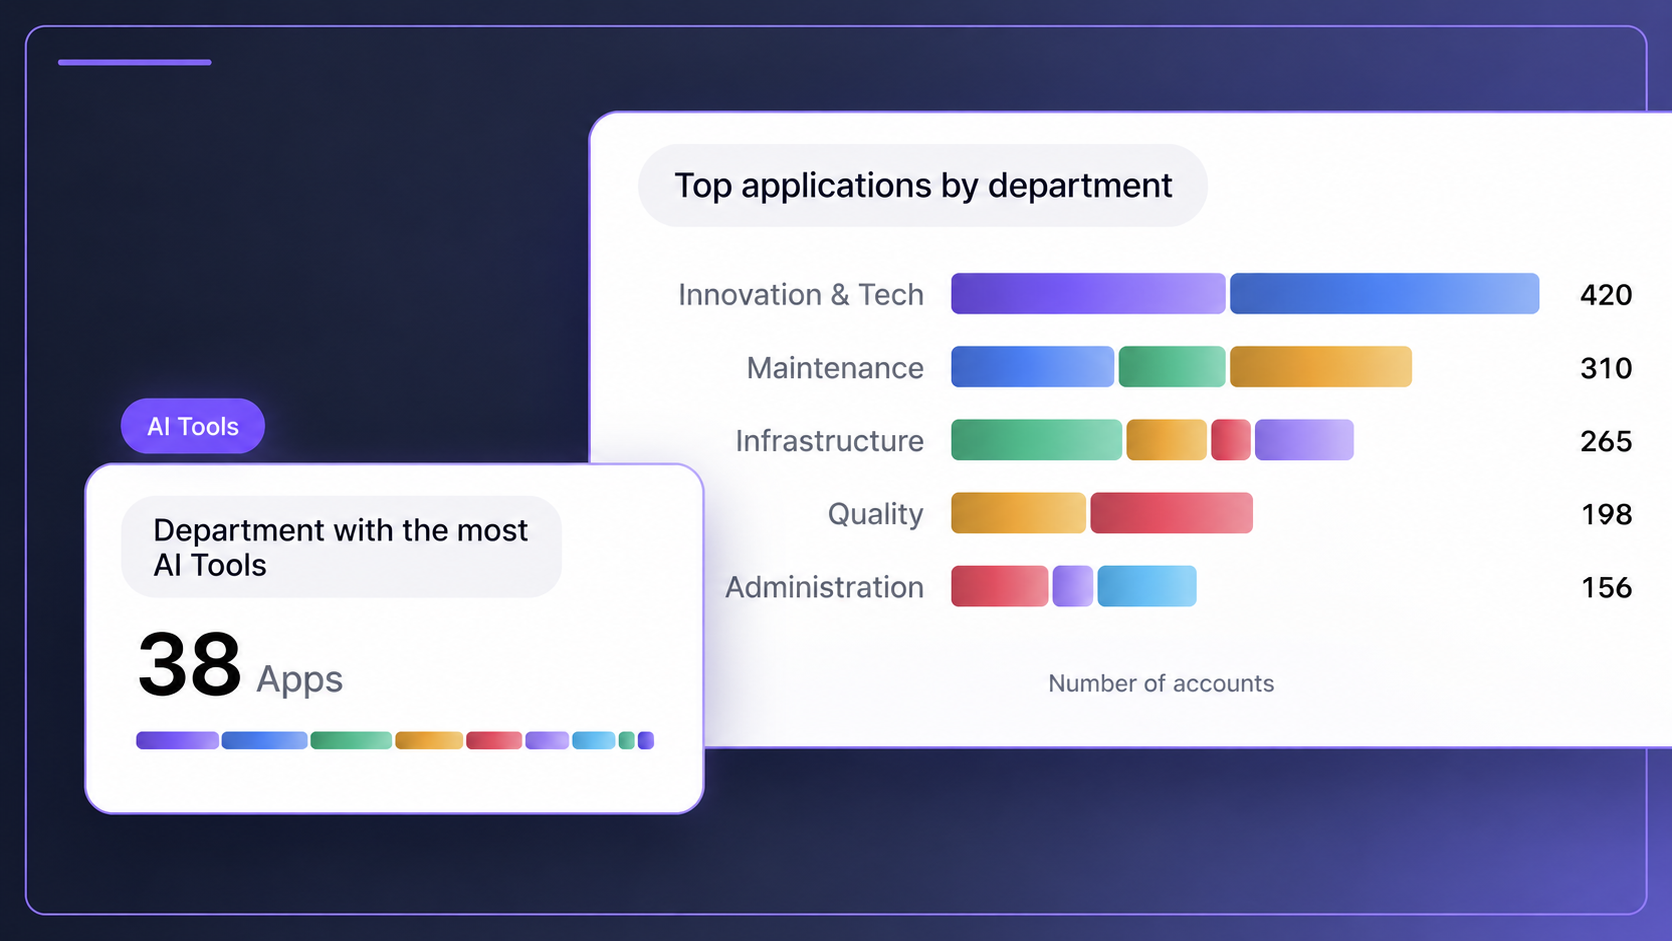
Who uses it? In which team? The departmental inventory provides context before you classify an application.
Review associated accounts, registered MFA methods and risk state in a person’s profile.
Prepare a departure
An OAuth connection can read information or act on an account. Review its permissions to make a decision in context.
View permissionsConnect applications and accounts to prepare discussions about subscriptions and usage.
Prepare a spend review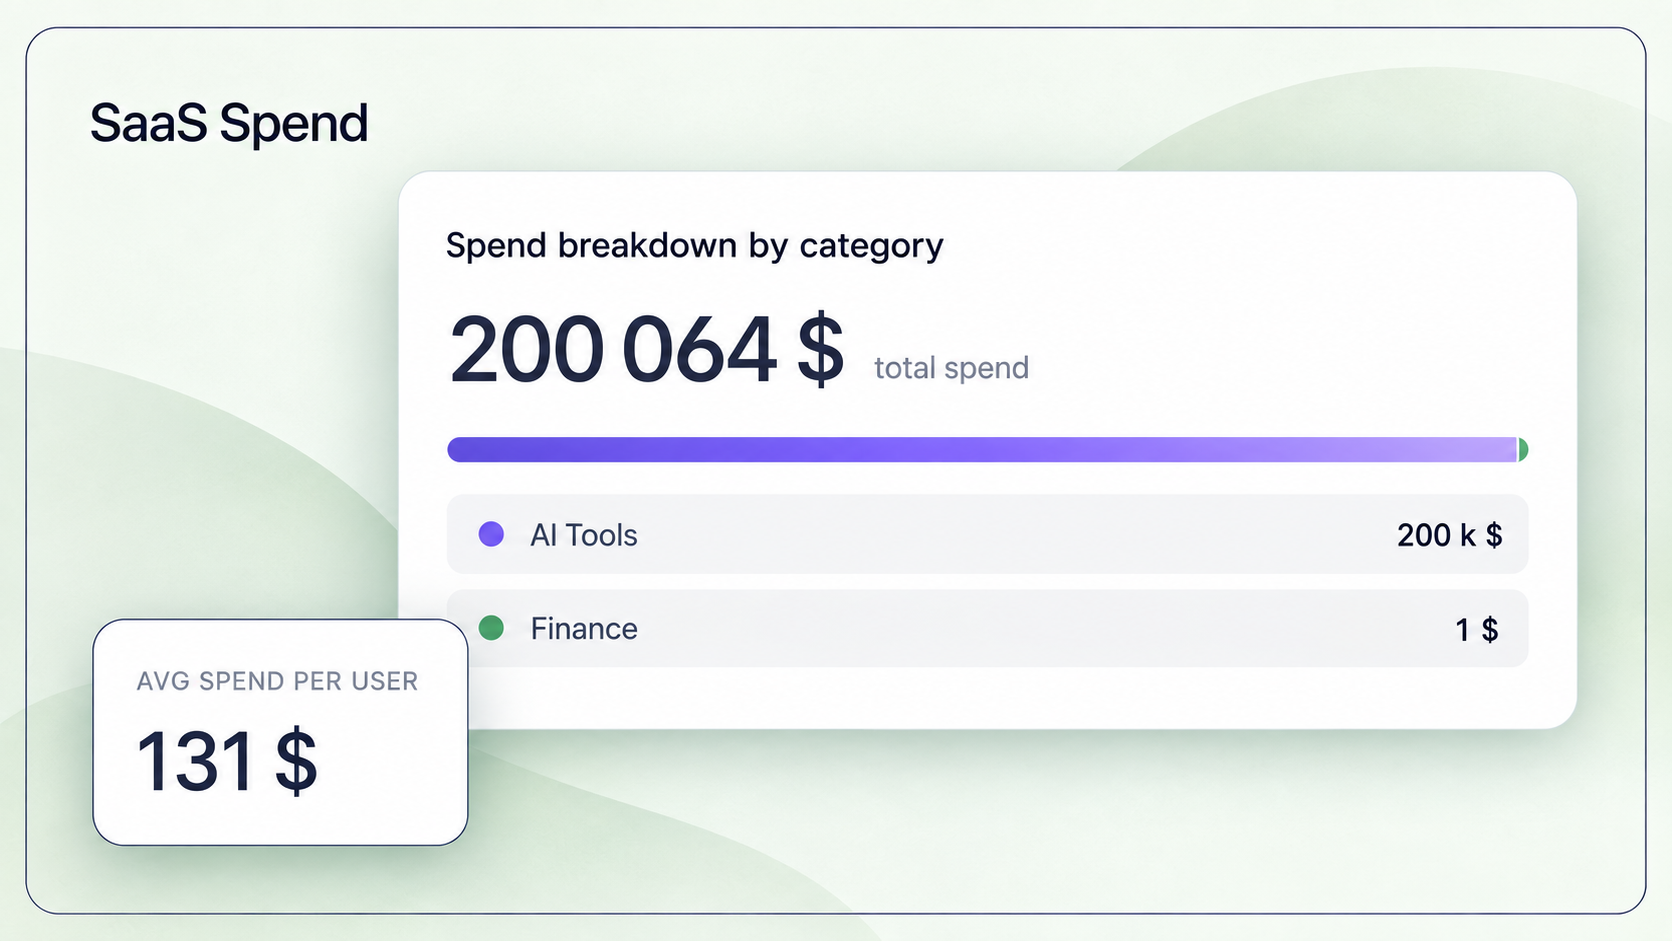
Connect domains, external services and available information to examine observations and prepare your priorities.
Explore the attack surfaceExamine available security signals, documents and dependencies before deciding in your context.
Review vendor securityReview posture findings and their related configurations. Choose connectors that match your actual environment.
Understand the checksPreview an action, confirm its scope and revisit its history. The context stays with the action.
Prepare a playbook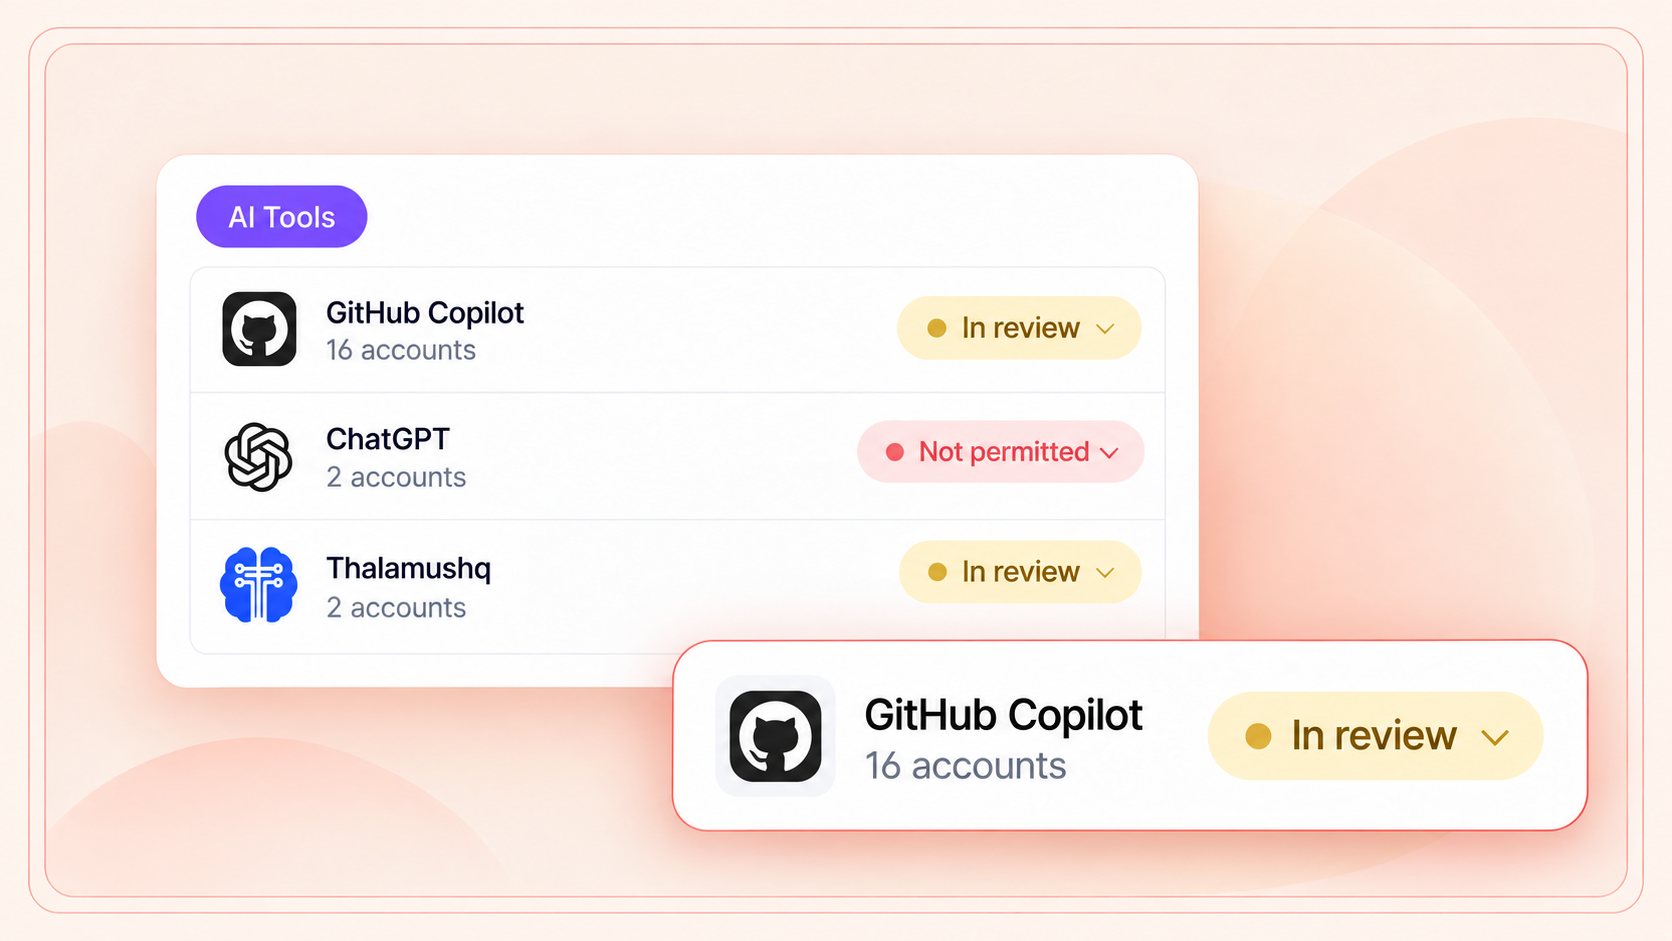
Applications, accounts and access.
The starting point for your next decisions.